Real-Time Threat Detection
Monitors security logs for anomalies, unauthorized access, and malicious behavior.

Cyber threats are constantly evolving, and businesses need real-time visibility into security events to protect critical systems. Neteam Solutions’ SIEM (Security Information & Event Management) delivers 24/7 threat detection, security analytics, and compliance monitoring — collecting and correlating data from firewalls, endpoints, cloud applications, and network devices with AI-driven threat intelligence and automated response for businesses across NYC, Manhattan, Queens, Long Island, and Astoria.
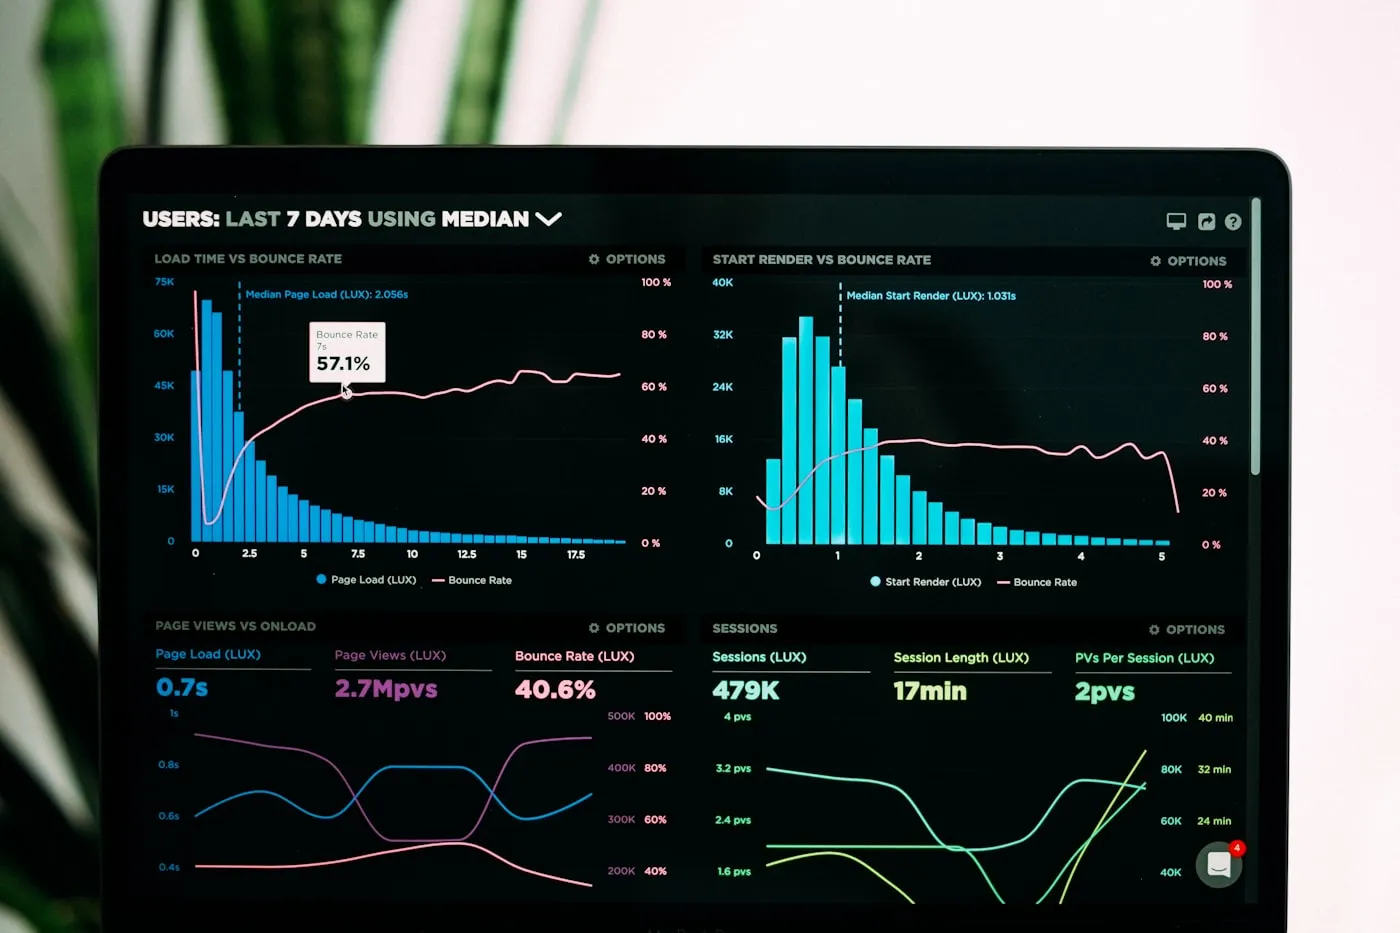
Illustrative example of correlated security events and automated response.
A SIEM turns the noise of firewalls, endpoints, cloud apps, and identity systems into a single, correlated timeline — so a brute-force attempt, an impossible-travel login, and a privilege escalation are recognized as one attack, not three unrelated alerts.
SIEM aggregates, analyzes, and correlates security logs from across your IT systems to detect suspicious activity, insider threats, and cyberattacks in real time.
Monitors security logs for anomalies, unauthorized access, and malicious behavior.
AI-driven analytics detect patterns that indicate cyber threats.
Triggers alerts and contains breaches before they escalate.
Helps meet HIPAA, PCI-DSS, SOC 2, and NIST cybersecurity standards.
Without a proper SIEM strategy, businesses are vulnerable to undetected cyber threats and compliance risks.
Real-time security alerts so threats are acted on fast.
AI-driven analytics detect zero-day threats, ransomware, and insider attacks.
Automates log management for HIPAA, PCI-DSS, NIST, SOC 2, and FINRA.
Collects and correlates security data across your IT infrastructure.
Identifies vulnerabilities, policy violations, and misconfigurations.
Full-spectrum visibility and automated risk mitigation across your environment.
SIEM aggregates, normalizes, and analyzes security data from across your stack:
Providing SIEM monitoring across NYC, Queens, Manhattan, Long Island, and Astoria.
Modern cyberattacks bypass traditional tools. Our AI-driven SIEM:
AI-driven detection and response for your entire environment.
Regulatory compliance is a major challenge for businesses handling sensitive data. Our SIEM helps you meet security mandates by:
Ideal for finance, healthcare, legal, and eCommerce across NYC, Queens, and Long Island.
Our managed SIEM solutions work seamlessly with your existing tools:
Comprehensive visibility and automated risk mitigation.
Our AI-driven SIEM analyzes security logs in real time to surface suspicious patterns, isolate compromised systems automatically, and flag privileged-account misuse — and it integrates with EDR and MDR to give you full-spectrum protection.
Talk to a SIEM specialist
Any business that processes sensitive data, operates in a regulated industry, or runs a hybrid cloud environment can benefit from SIEM. These are examples, not a limit. We provide SIEM across NYC, Manhattan, Queens, Long Island, and Astoria.
Secure corporate networks, cloud environments, and remote workforces.
HIPAA-compliant data protection and secure patient/client records.
Protect against identity theft, fraud, and insider threats.
Secure POS systems, online transactions, and customer payment data.
Serving NYC businesses since 2001, Neteam Solutions offers fully managed SIEM to detect, prevent, and respond to cyber threats.
Fully managed cybersecurity for NYC and Long Island businesses.
Advanced machine learning-driven threat detection.
Tailored to your business size, industry, and compliance needs.
Works with Splunk, IBM QRadar, Microsoft Sentinel, and Elastic SIEM.
SOC experts actively investigate and remediate threats.
Automated compliance reports for PCI-DSS, HIPAA, SOC 2, NIST, and FINRA — plus forensic-grade log retention and real-time dashboards that track your security posture and risk levels, so you’re always ready for an audit.
Schedule a free consultationCybercriminals increasingly target unprotected networks, cloud environments, and identity systems. Without centralized security management, businesses risk breaches, compliance violations, and financial loss. Let Neteam Solutions help you secure your IT infrastructure.